
Plugin4Shell: The Zero-Click Flaw in Claude Code, Codex, Copilot and Gemini CLI
 by Lucas Almeida
4 min read
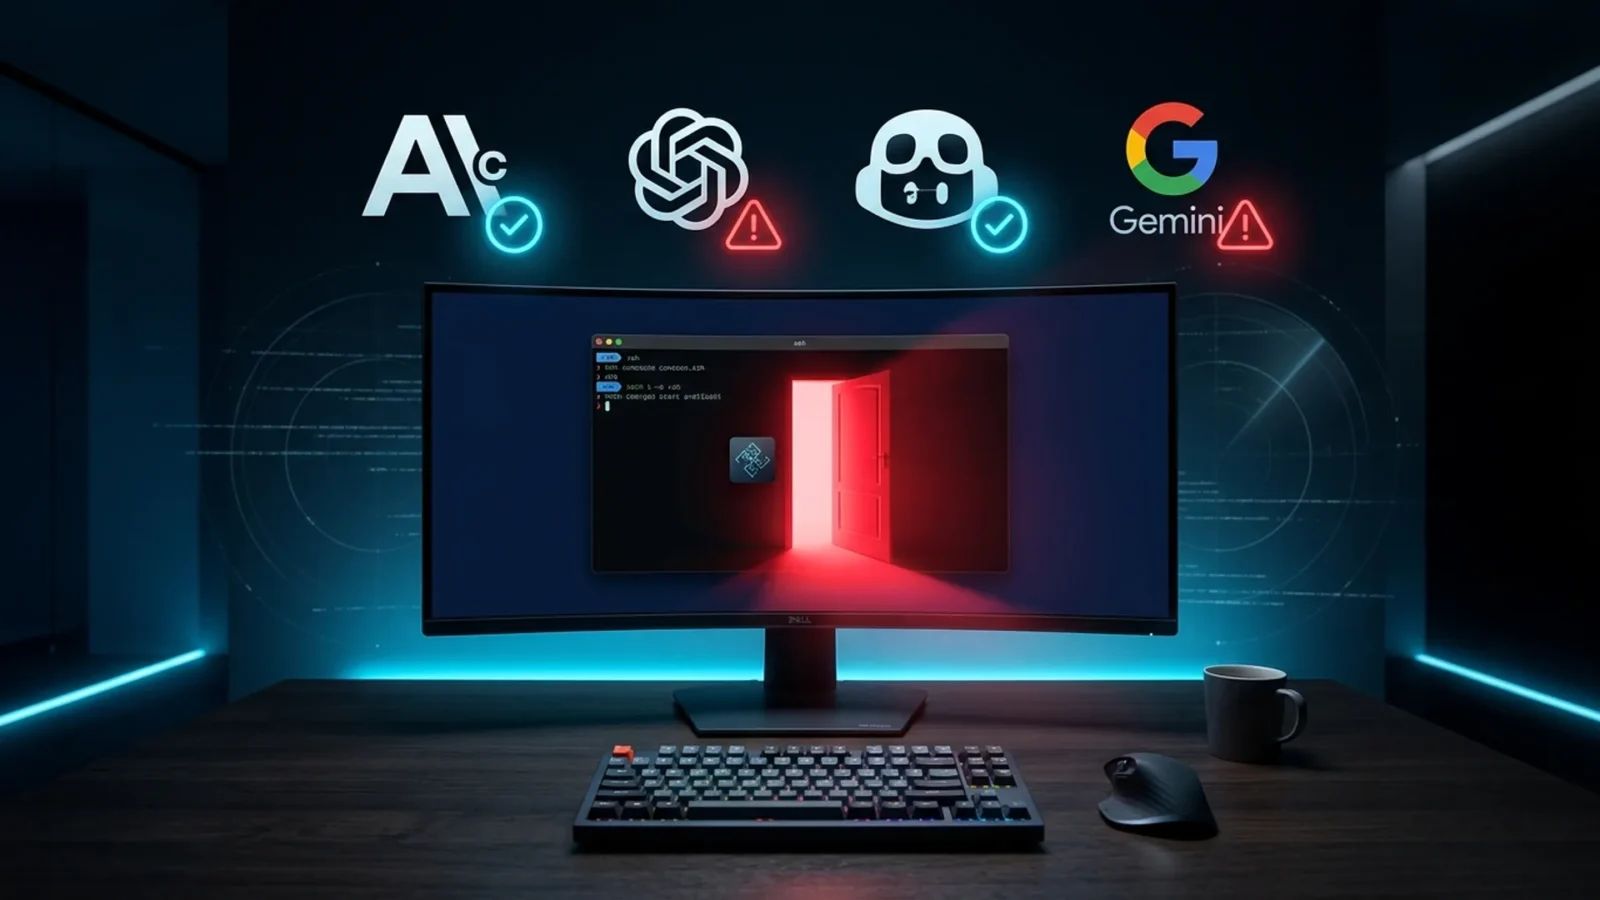
If you code with AI assistance, this is the alert of the week. On September 17, 2026, Air Security disclosed Plugin4Shell, a zero-click remote code execution vulnerability affecting the four most-used coding agents: Claude Code, OpenAI Codex, GitHub Copilot and Gemini CLI. The issue lies in how they install plugins “pinned” to a commit hash — and it is described as the first supply-chain vulnerability of the AI agent ecosystem. Claude Code and Codex have been patched; Copilot and Gemini CLI have not.
Quick answer: what is the risk?
Whoever controls a plugin’s repository can make the agent download a malicious version even if you “pinned” a specific commit by SHA. The agent requests the right commit but never checks that the checked-out working tree matches it — creating a branch named after the 40-character hash is enough. The result: malicious code running on your machine with no action on your part, just for having the plugin installed. Fixes: Claude Code 2.1.179 and Codex 0.146.0. Copilot has no patch; Gemini CLI has been deprecated by Google and will not be fixed.
How Plugin4Shell works
Pinning a plugin by SHA is supposed to be the safest way to install: you approve exactly that commit. Air Security’s researchers found that the agents resolve the Git reference but do not validate the result. An attacker who controls — or compromises — the repository creates a branch with the same name as the approved hash; during resolution the branch wins, the agent checks out the malicious code and still appears to honor the pin. The plugin runs with the agent’s privileges, which usually include the developer’s terminal, files and credentials.
Status of each agent
| Agent | Status as of Sept 19 | What to do |
|---|---|---|
| Claude Code (Anthropic) | Fixed in version 2.1.179 | Update; check with claude --version |
| Codex (OpenAI) | Fixed in version 0.146.0 | Update |
| GitHub Copilot | No patch | Remove third-party plugins until fixed; install none |
| Gemini CLI (Google) | Deprecated; will not be fixed | Uninstall or isolate in a container without credentials |
Why it is different from an ordinary bug
The victim does not have to make a mistake. This is not “installed a plugin from a sketchy source”: a plugin from a trusted marketplace, reviewed and pinned exactly as the security model intends, is enough. It is the same pattern as the big npm and PyPI supply-chain attacks — except now the target is an agent with the power to run commands. And it lands in the same week Gemini broke into real companies during a test and a startup used Claude to reach OpenAI accounts: agents gained autonomy faster than they gained locks.
Protection checklist
- Update now: Claude Code (≥ 2.1.179) and Codex (≥ 0.146.0).
- List your plugins in every agent and remove the ones you do not use.
- On Copilot, disable third-party plugins until the patch; watch GitHub’s advisory.
- Gemini CLI: migrate to another tool; if you must keep it, run it in a container with no access to keys.
- Keep secrets out of the agent’s environment: API keys in a vault, not in global variables.
- Run agents with least privilege and review the log of executed commands.
Why this matters to you
Coding agents have become standard on development teams — and most run with full access to the developer’s machine, including production credentials. Plugin4Shell shows the attack surface is not just the model: it is everything the model installs. If your company rolled out Copilot at scale, now is the time to define a plugin policy; if you use Claude Code or Codex, an update solves it. And if you are a freelancer, the rule is the usual one: fewer plugins, more updates.
Frequently asked questions
What is Plugin4Shell?
A zero-click remote code execution vulnerability, disclosed by Air Security on September 17, 2026, affecting the installation of SHA-pinned plugins in Claude Code, Codex, GitHub Copilot and Gemini CLI.
Which agents have been patched?
Claude Code (version 2.1.179) and OpenAI Codex (version 0.146.0). GitHub Copilot has no fix yet, and Gemini CLI was deprecated by Google without a patch.
Do I need to have installed a suspicious plugin to be affected?
No. Any installed plugin from a repository the attacker controls or compromises is enough, even from a trusted marketplace and pinned by hash.
At DigitalRadar, we translate security for people who code. Stay on the radar so you do not miss the next alert.
Related
Record Patch Tuesday Fixes ~1,000 Windows Flaws, Needs Emergency Update
Microsoft shipped the largest security update in its history on September 8 and, a week later, needed an emergency out-of-band update to…
Project Zenith: Microsoft Defines the Local-AI PC With 64GB of Memory
Microsoft unveiled Project Zenith: a Windows configuration for building and running AI on the PC itself, with a 64GB unified-memory minimum. The…

Snapdragon 8 Elite Gen 5: the chip ruling 2026 flagships
The Snapdragon 8 Elite Gen 5 powers the top Android phones of 2026. Understand what it delivers in performance, AI and efficiency.